On this page
- Start with data and requirements
- 1. Identity, sessions and recovery
- 2. Authorization and company isolation
- 3. Transport encryption is not end-to-end encryption
- 4. Understand processing locations and connections
- 5. Test export, departure and deletion
- 6. Require evidence for certification and recovery commitments
- A practical acceptance checklist
Virtual-office security depends on who can enter, what they can see or change, and how information moves, remains stored and is deleted. A 3D office design does not establish file protection, and “encrypted” does not answer every security question. Assess workflows, controls, evidence and limitations together.
This is a buyer's checklist, not an independent audit or penetration test. HyoNova-specific controls are attributed to company publications. Screenshots show a fictional demo on production version 87663bba1 captured on 28 October 2026. A successful sign-in alone is not approval to upload sensitive records.
Start with data and requirements
List internal discussions, client files, contracts, employee records and finance data you intend to store. Identify restricted categories and non-negotiable requirements, such as a particular authentication method, processing location or certification. Collaboration features do not override those requirements.
Name a decision owner. Even a small company needs responsibility for recovery, shared links and offboarding. A tool cannot supply an organizational policy the company has not defined.
1. Identity, sessions and recovery
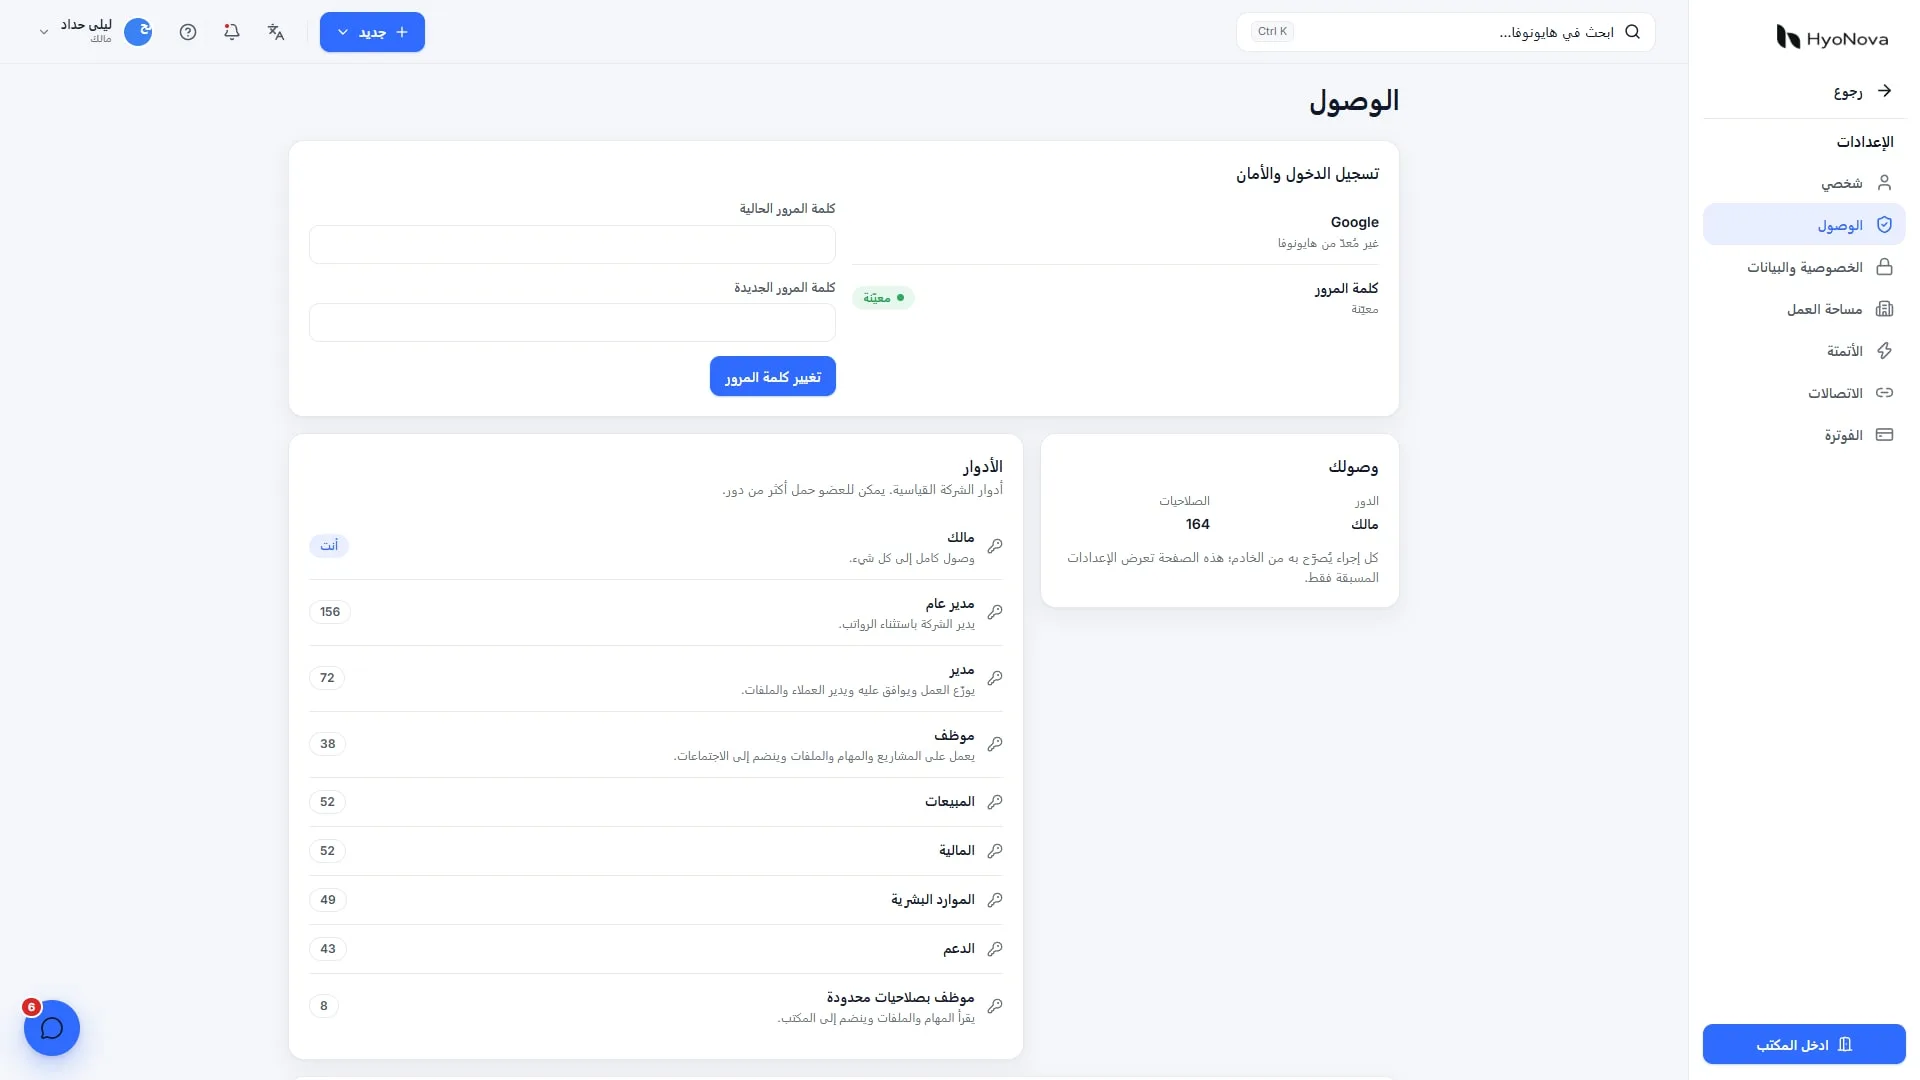
Ask how members authenticate, recover access and end sessions, including when they leave. Separate company roles from protection of an individual's account. Test recovery using fictional data without sending passwords to colleagues or support.
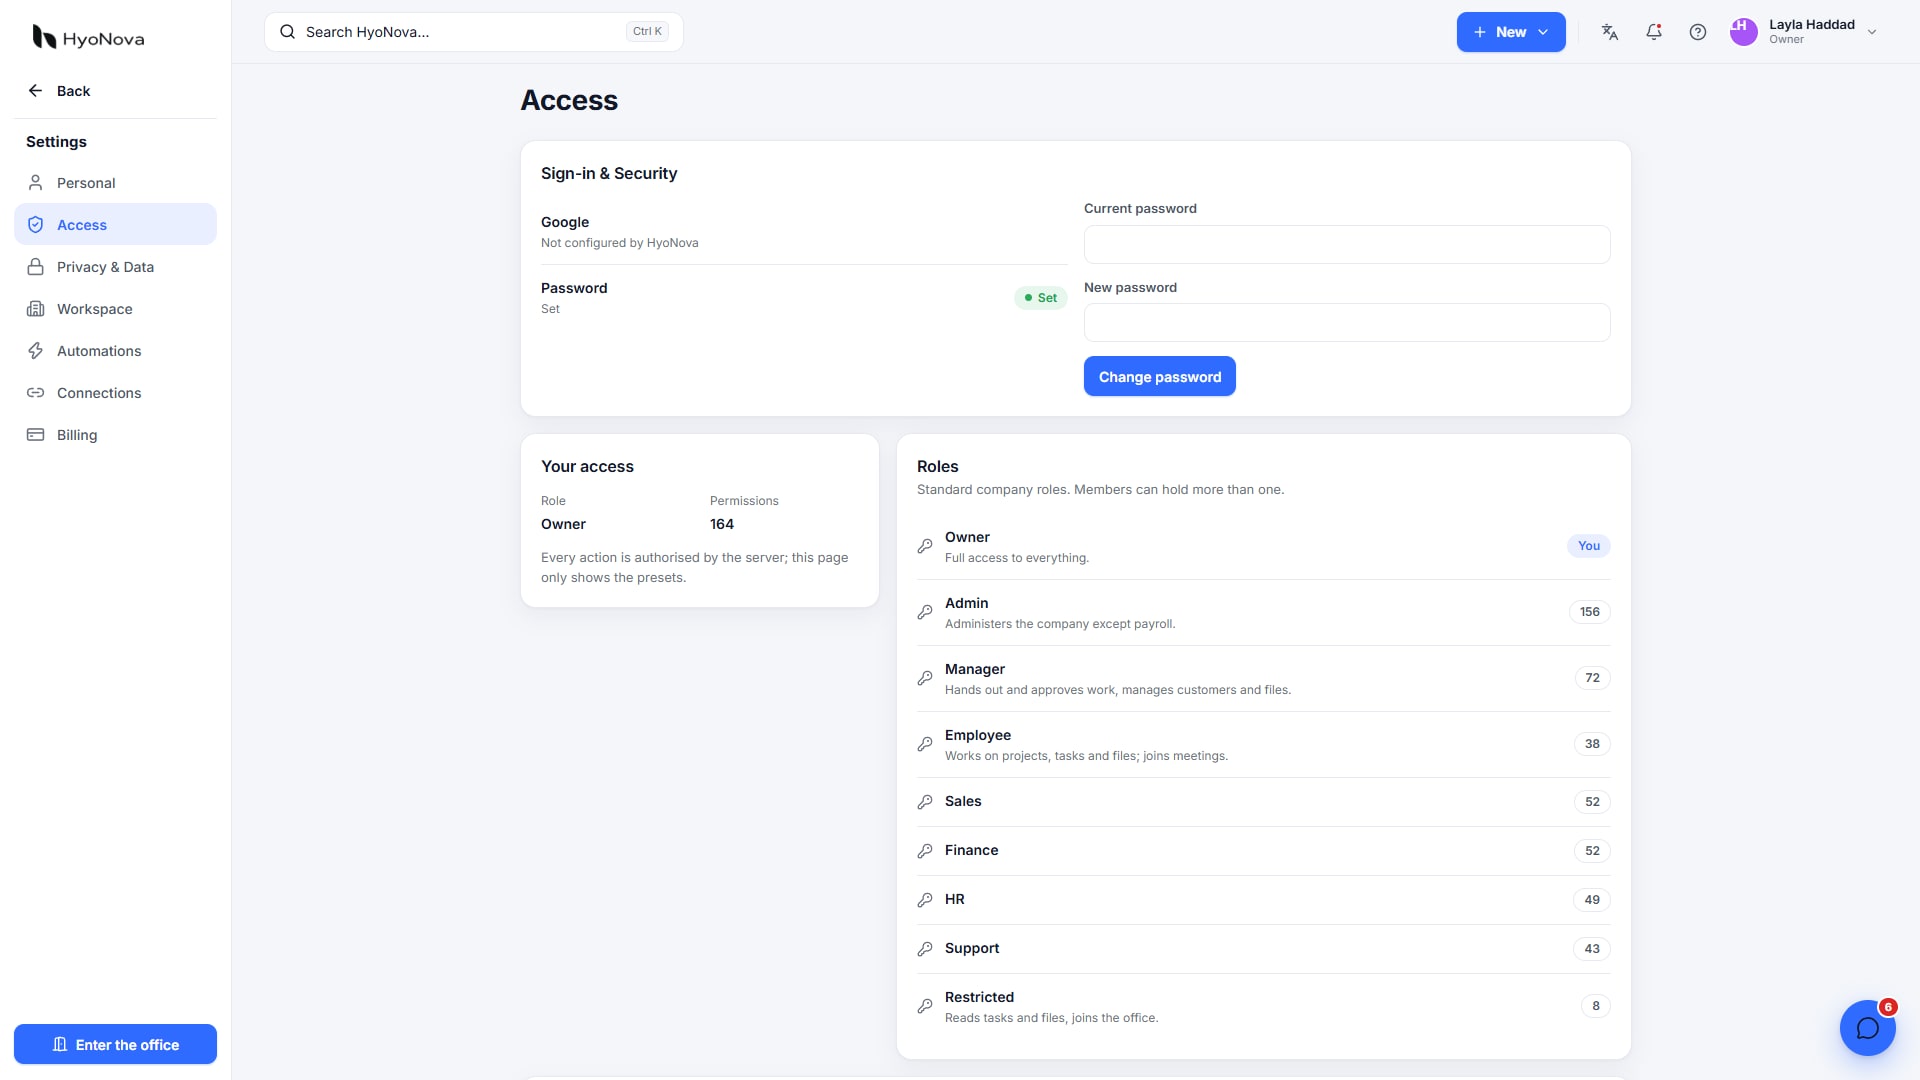
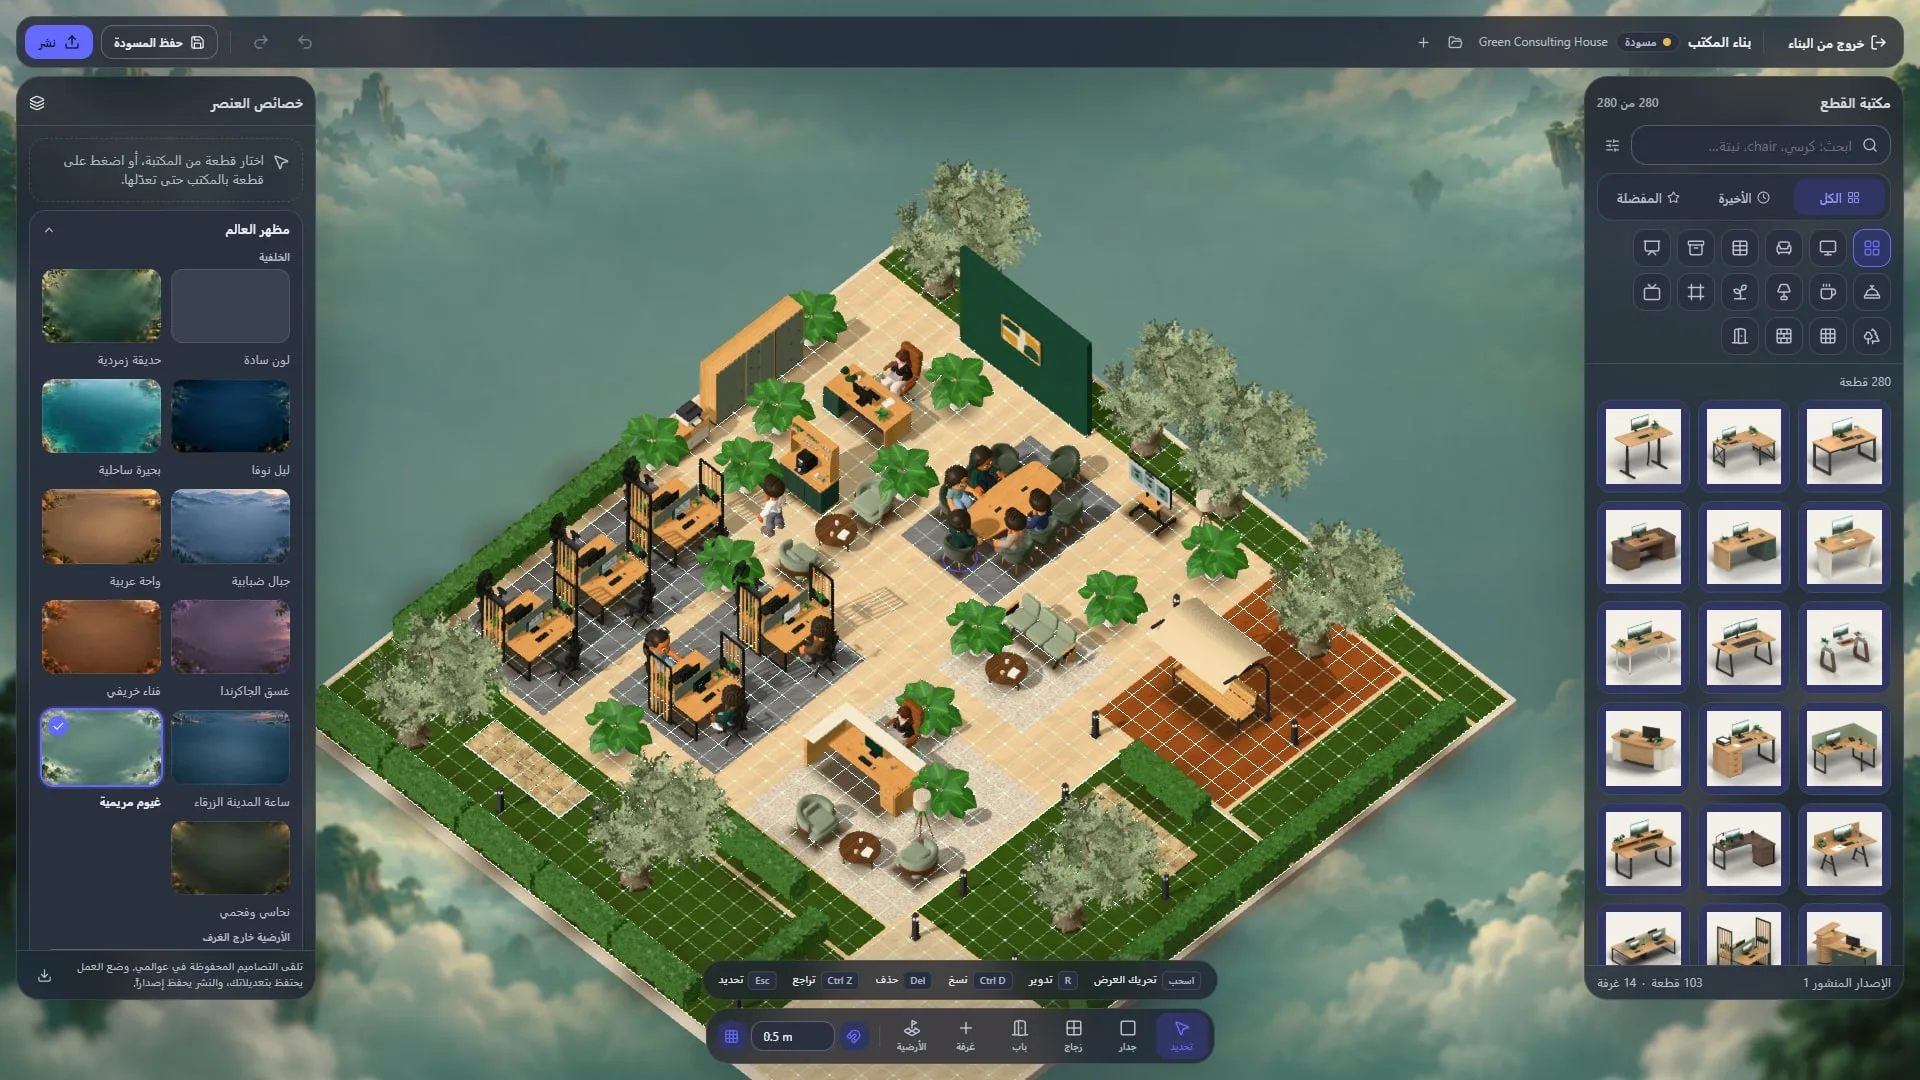
Actual product capture from a local demo on production version 87663bba1, captured on 28 October 2026. Fictional data.
A published limitation matters: email-and-password sign-in in HyoNova currently lacks two-step verification and passkeys. Enterprise offers SAML SSO and SCIM. If MFA is mandatory, verify identity-provider requirements and contractual fit rather than assuming a missing control can be enabled from the screenshot.
2. Authorization and company isolation
Ask how permissions are enforced server-side and how organizations are isolated, then test authorized accounts against fictional records. Hidden buttons are not sufficient evidence. Can a restricted member open a record directly? Can someone grant more authority than they hold? Do not test other companies' records or systems without permission.
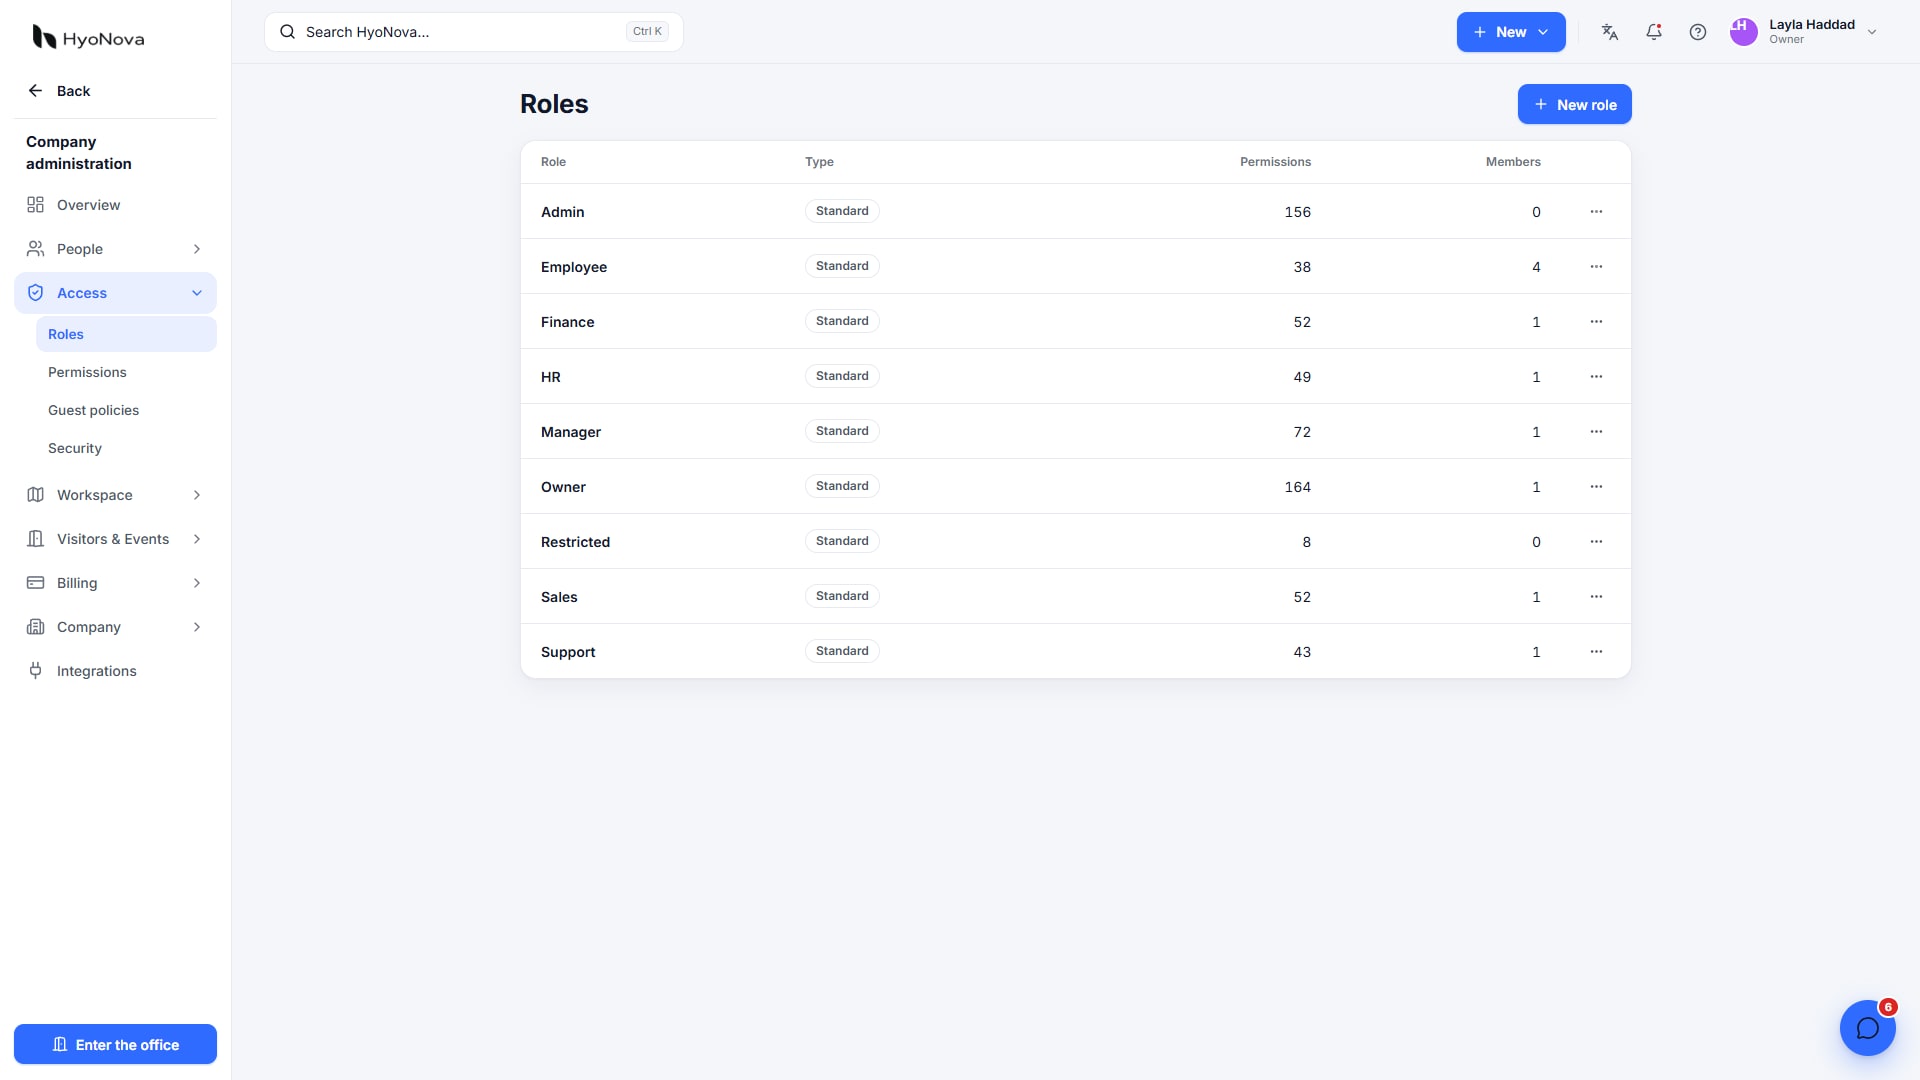
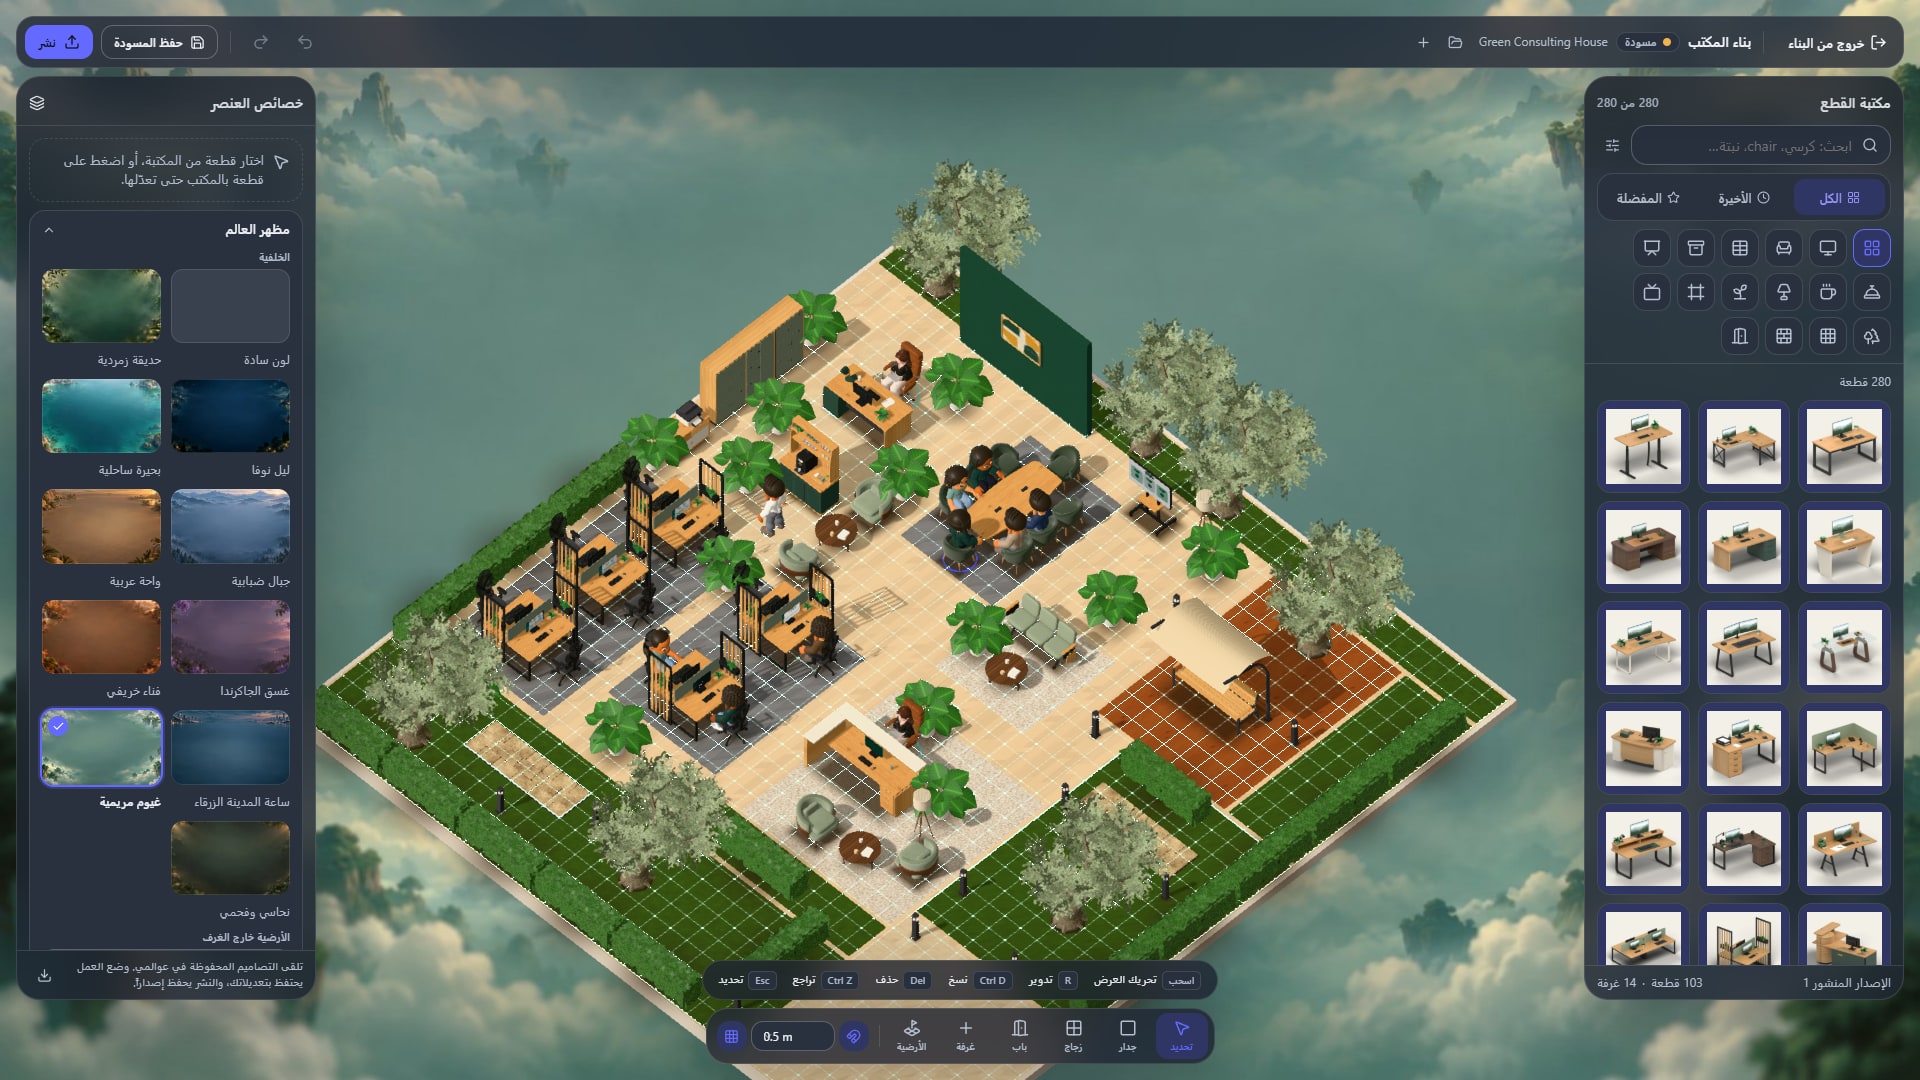
Actual product capture from a local demo on production version 87663bba1, captured on 28 October 2026. Fictional data.
Area | Published HyoNova control | Buyer's check |
|---|---|---|
Isolation | Database row-level security | Request scope and appropriate supporting evidence |
Permissions | Server checks, standard and custom roles | Test read, change and approval operations with restricted accounts |
Guests | Scoped links with expiry controls | Check destination, expiration and revocation |
Data | Encryption in transit and at rest | Ask about keys, backup copies, export and processors |
3. Transport encryption is not end-to-end encryption
HyoNova states that calls and meetings are encrypted in transit, not end to end. Protecting the connection is different from making content technically inaccessible to the service provider. Define permitted meeting content accordingly.
Ask separately about recording: who starts it, who can access it and when it is deleted. An entry audit log is not an audio recording. A test scenario with no recording does not establish recording behavior across every workflow.
4. Understand processing locations and connections
The published primary application deployment is AWS Frankfurt, but that does not establish EU-only processing for every public-website request, selected provider or AI action. Read the provider register alongside the applicable agreement and ask which data categories reach each service.
The AI policy describes authorized context being sent to the configured provider when assistance is invoked. Do not assume universal zero retention. Define permitted knowledge, human review, escalation and workflow stopping rules.
5. Test export, departure and deletion
Export a sample and open it outside the account. Remove a test member and review work ownership, guest links and integrations. Ending access is not deletion of company-owned work, and disconnecting a mailbox does not delete original messages at the mail provider.
The retention policy distinguishes record categories and agreements, and active-service deletion from immediate erasure of every backup. Request the relevant schedule, authorized deletion route and exceptions instead of inventing one universal retention period.
6. Require evidence for certification and recovery commitments
HyoNova explicitly states that it does not hold SOC 2, ISO 27001 or an independent penetration-test certificate, and does not promise a general recovery guarantee or SLA without separate evidence or agreement. Resolve mandatory procurement requirements before uploading data or contracting. A hosting provider's logo is not certification of the application itself.
A practical acceptance checklist
Least necessary roles, with tested viewing, editing and approval boundaries.
Authentication and recovery appropriate for company requirements.
Guests with known scope, expiry and ownership.
An explicit meeting recording and sharing policy.
Provider inventory, permitted AI context and approval and escalation limits.
A tested export, offboarding route and understood retention, deletion and recovery schedule.
Current evidence for required certification or contractual promises, or an explicitly documented gap.
Read the official security page, data processing addendum and linked policies. Start with a scope justified by evidenced controls and expand after review. Security remains an ongoing decision supported by tools, evidence and accountable people.